Network administrator
“I have no time to learn one more tool.”
One install, one login, a panel in Uzbek. Every panel action is also an fsctl command, for scripts and automation.
Early Access · pre-1.0 product
FireSecurity runs next to your existing firewall in shadow mode: for every connection it reports what it would have done, and never touches the traffic. A modern firewall, logs and inventory to replace Kerio or pfSense: one panel, in Uzbek.
01
FireSecurity takes a copy of the traffic, through a switch port mirror (SPAN) or a transparent bridge. The old firewall stays where it is.
02
Traffic is not touched during the trial. You decide after you have seen the report.
S06.1, S06.5 — netns lab
03
If you do not like the report, you stop, and there is nothing to switch off. If you do, you cut over by the runbook, with a confirmation window on every change and automatic rollback.
04
When the console is switched off, the license file is deleted, the license has expired or its signature is broken, real traffic is sent and lost packets are counted.
QA-T-500 — on every change and every night
A sample network, drawn — not a measurement.
Live map
Every day thousands of connections hit the edge of a network. FireSecurity stops them at the gateway itself and writes each one to the audit log. Spin the globe.
Blocked
Passed
Event stream
Blocked trafficNormal traffic
Who it is for
The administrator picks the firewall, the head of IT approves it, and the finance director or the rector pays for it. Each gets their own answer.
“I have no time to learn one more tool.”
One install, one login, a panel in Uzbek. Every panel action is also an fsctl command, for scripts and automation.
“Why does finding the cause of an incident take hours?”
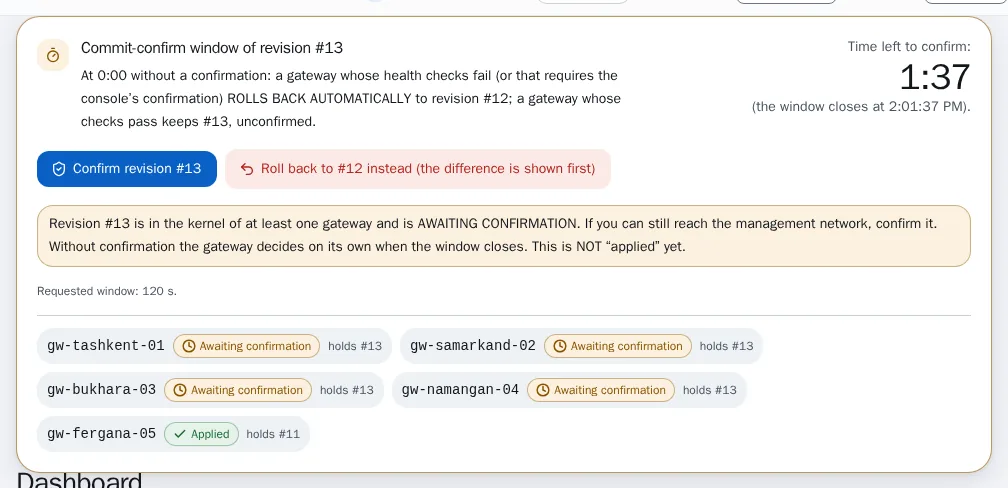
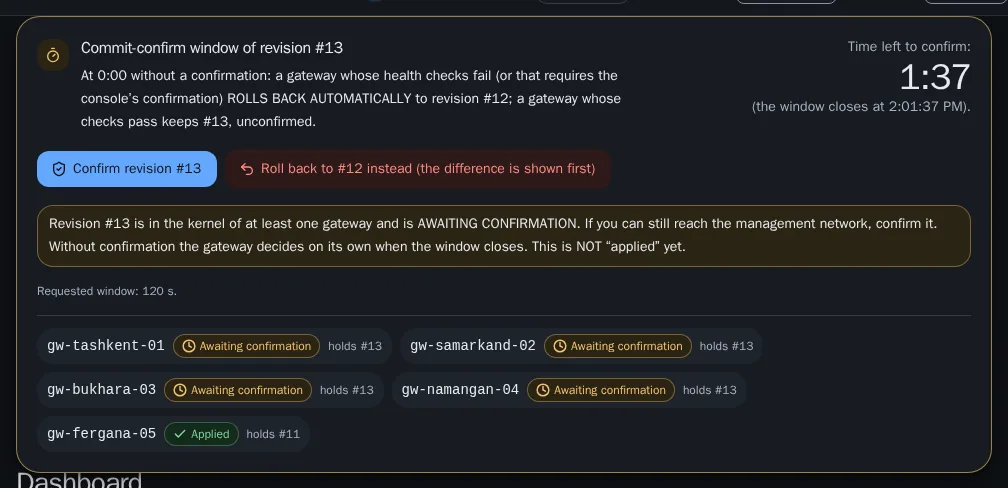
From a log line, one click takes you to the rule that produced it and to the version of the rule set. Every change is applied with a confirmation window and rolls back by itself if not confirmed.
Compare with the free stack“What happens when the subscription ends or the exchange rate rises?”
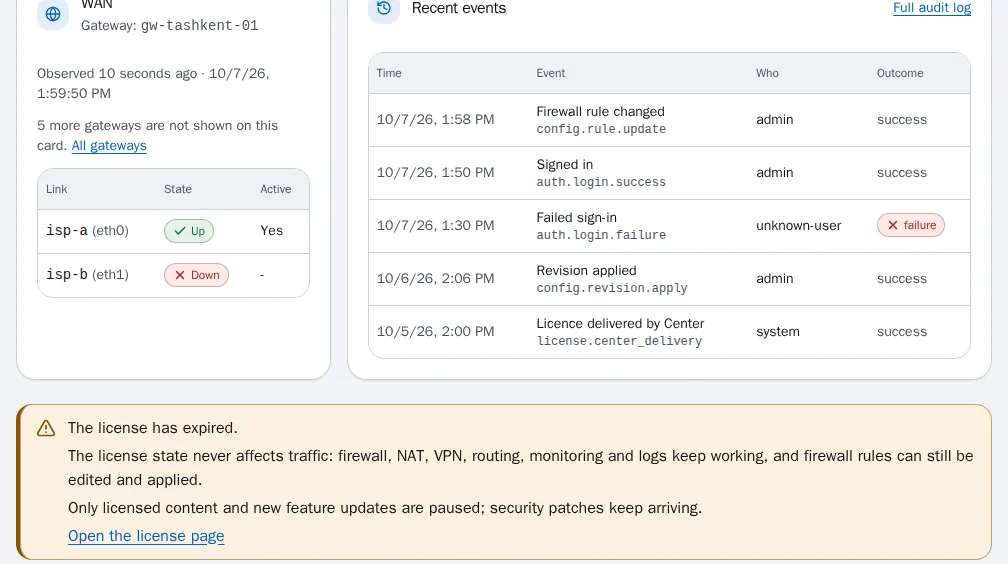
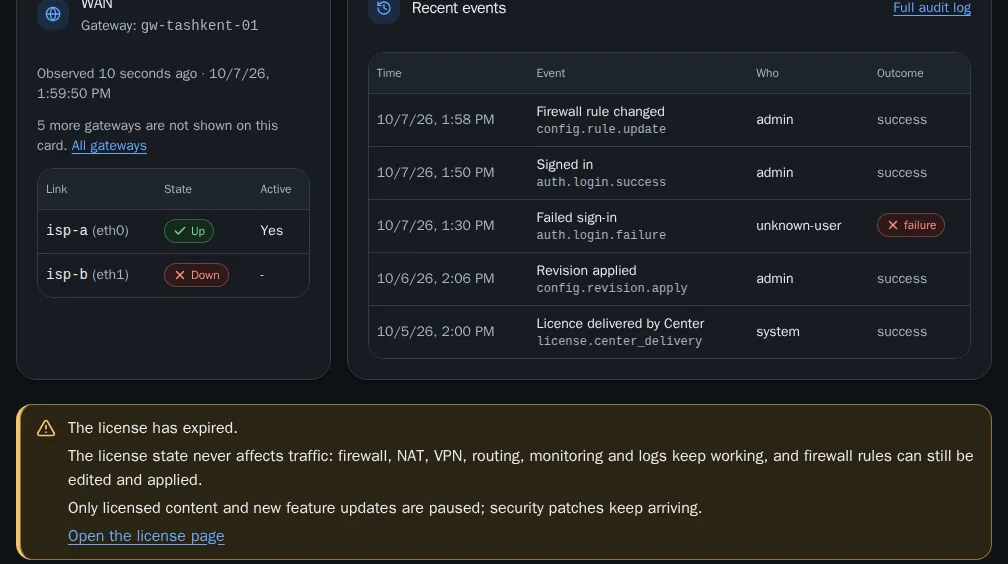
The price list and payment are in som. Forwarding, NAT, VPN, monitoring and logs keep working after the license expires: a late payment does not leave the organization without a network.
Work out the cost of ownership with your own numbers“Can I prove who changed what, and when?”
Every change goes into a hash-chained audit log. An entry that was edited, deleted or moved shows up in the fsctl audit verify check.
Shadow trial
The objection a new vendor hears most is “risk”. Shadow mode takes that risk out of the trial: your existing firewall keeps working, and FireSecurity only observes and reports.
FireSecurity takes a copy of the traffic, through a switch port mirror (SPAN) or a transparent bridge. The old firewall stays where it is.
A Kerio, pfSense or OPNsense configuration is imported. You get a report on every rule: migrated, approximately migrated, needs manual work or ignored — and why.
The report answers three questions: which traffic the new policy would have blocked, which traffic no rule matched, and which rules never fired at all. A daily summary arrives in Telegram.
If you do not like the report, you stop, and there is nothing to switch off. If you do, you cut over by the runbook, with a confirmation window on every change and automatic rollback.
Not touching traffic is a test, not a promise. First we check that enforce mode really blocks, then that observe mode passes every packet unchanged. On a transparent bridge the outgoing frame is compared byte for byte with the incoming one.
S06.1, S06.5 — netns lab
Worth knowing: a port mirror sees addresses after NAT and does not model MSS differences. The panel states these blind spots itself, at the top of the report. Long observation on a real network will be measured in the first pilot.
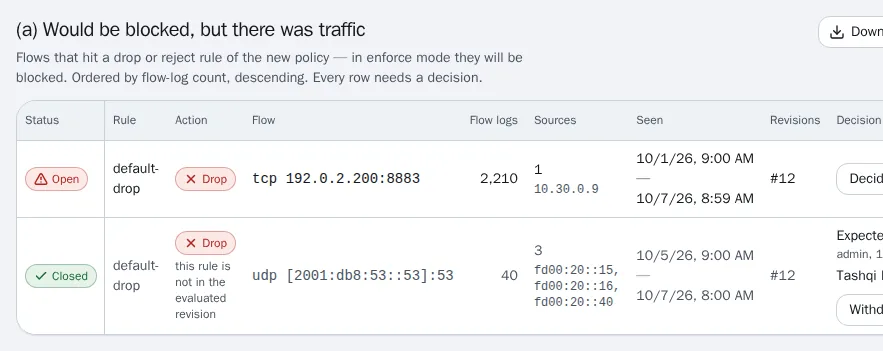
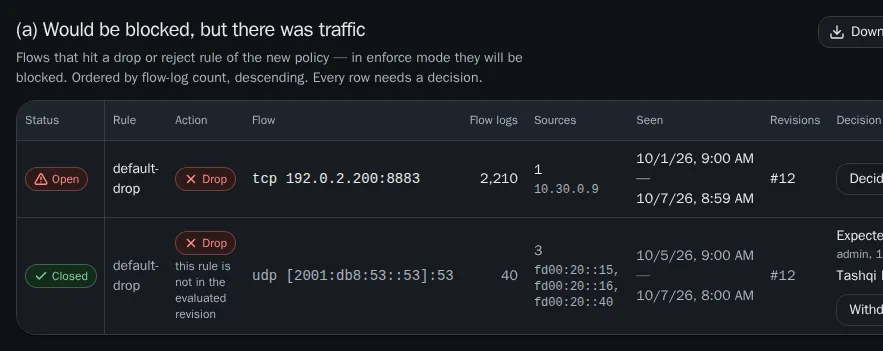
Traffic is not touched during the trial. You decide after you have seen the report.
Your data stays with you, and the contract says so. Today: the audit log, inventory and shadow report as CSV, and metrics in Prometheus format.
Exporting the configuration as YAML and the logs in an open format is planned before 1.0.
A discount off list and a free move to 1.0. Only modules proven in a pilot; the list is an annex to the contract.
Traffic is not touched and nothing is switched off.
Cost of ownership
Our main competitor is not FortiGate but the free stack: pfSense or OPNsense, Zabbix, Grafana, Graylog, Wazuh. Its cost is not in the license but in administrator time. The calculation below uses only the numbers you enter; we add nothing of our own.
Your current stack per year
—
This is the cost of your current stack. We do not promise in advance how much FireSecurity will save: in a pilot the same components are measured before and after, and the success criterion is written down at the start of the pilot.
Request a trial with this calculationHonest comparison
A one-sided table convinces no one. The free stack is built from good tools, and the places where it wins are written down here too.
| Criterion | Free OSS stack | FireSecurity |
|---|---|---|
| License price | Zero its strength | Annual subscription, in som; price on request |
| Familiarity | Administrators know it; plenty of guides and community its strength | A new product; the panel is in Uzbek, but it takes learning |
| Maturity | Proven for years in thousands of networks its strength | Pre-1.0, on Early Access terms |
| Breadth of features today | Broader: IPS, SIEM, many plugins its strength | Firewall, NAT, multi-WAN, logs, inventory, audit; IPS in 1.0 |
| Install and upgrade | Each tool is installed and upgraded separately | One install, one upgrade |
| Login and permissions | Separate in each tool | One login, roles, LDAP groups |
| From incident to cause | By hand across tools, matching on time and IP | From a log line to the rule and its version, in one click |
| Firewall changes | Depends on the tool; no single confirmation and rollback across the stack | Every change: view the diff, confirmation window, automatic rollback if not confirmed |
| Audit | Each tool has its own log | One hash-chained log, with a verification command |
| Who to turn to | A forum or paid support from abroad | A local team, in Uzbek and Russian; best-effort SLA in Early Access |
| Dependence on one person | If the person who built the stack leaves, the knowledge leaves with them | One documented product and its vendor |
| Vendor lock-in | None — open source its strength | Exit guarantee in the contract; part of the export is still on the roadmap |
When it is better to stay on the free stack. If your stack runs steadily, the person who built it is still on the team and it is documented, and what you need right now is IPS or SIEM correlation, do not rush. Today FireSecurity is strong not in breadth of features but in one panel and controlled change.
Product
Early Access covers the firewall and the daily work around it: rules, logs, inventory, audit and notifications. For the other modules, the release each arrives in is written down.
Zones and rules; the rule set is replaced in a single transaction. Several uplinks, health checks and failover.
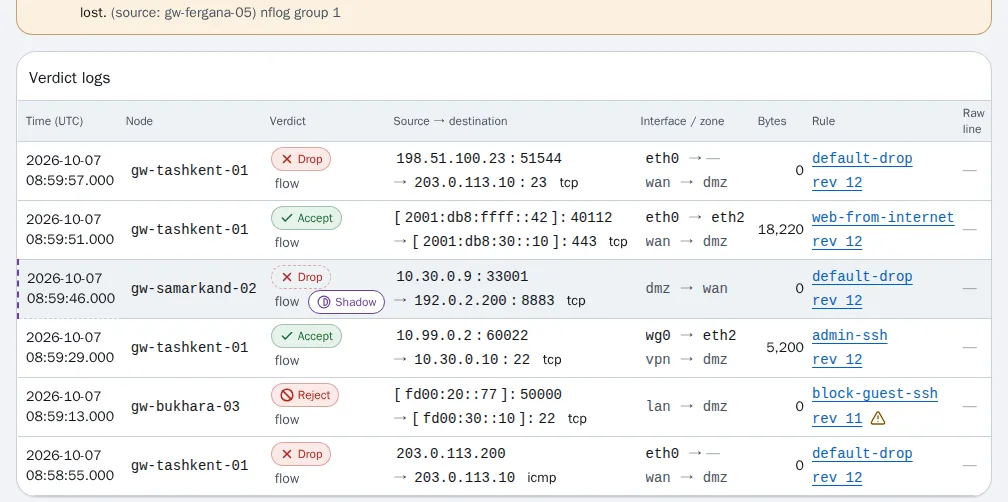
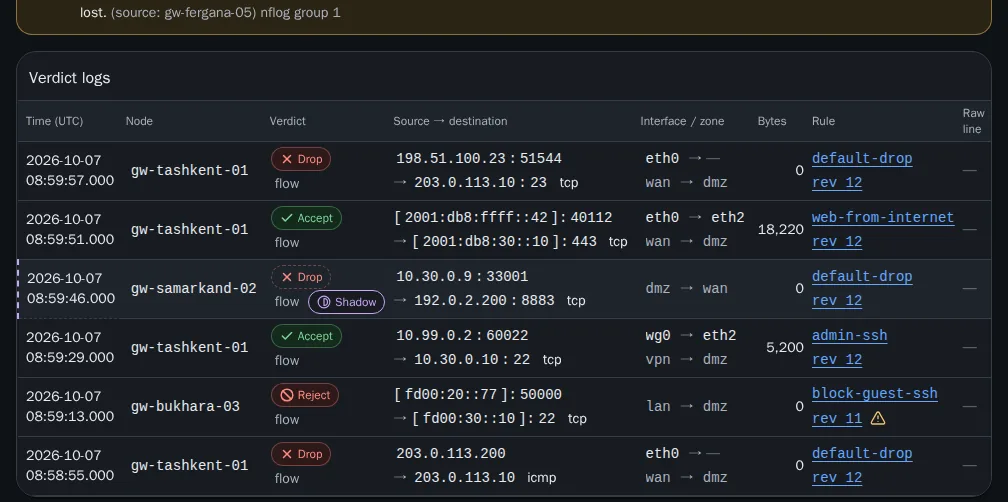
Firewall verdicts and syslog from external devices. From any verdict line, go to the rule that produced it.
A list of the devices the gateway has seen (ARP/NDP and DHCP), with CSV export.
Import from Kerio, pfSense and OPNsense; the shadow report; cutover and rollback runbooks.
Telegram and email: WAN switchover, gateway offline, mode change, the daily shadow summary.
The panel is in Uzbek, Russian and English. Every panel action is in the fsctl CLI too.
| Module | When | What it does |
|---|---|---|
| Firewall Core, NAT | 1.0 | Zones, rules, NAT; the rule set is replaced atomically |
| Multi-WAN | 1.0 | Several uplinks, health probes, automatic failover |
| WireGuard VPN | 1.0 | Site-to-site tunnels |
| Monitoring, metrics, dashboards | 1.0 | Node and interface state, uptime |
| Logs and search | 1.0 | Verdict logs and external syslog, search and aggregation |
| Inventory | 1.0 | A list of the devices on the network |
Proxy Manager, fsctl CLI | 1.0 | Reverse proxy; every panel action is in the terminal too |
| Identity, NAC (monitor), DNS, DHCP, IPAM | 1.0 (Pro) | Users, access control, address management |
| IPS (Suricata-based) | 1.0 (Pro) | Attack detection |
| Server Manager, certificates, reports | 1.0 (Pro) | Servers and PKI work |
| PKI base, gateway HA, eBGP base | 1.0 (Enterprise) | High availability and routing |
| WAF (Coraza), config backup | 1.1 | Web application protection; configuration backup |
| Remote access, password vault, NAC closed | 1.2 | Remote access and secrets |
| TLS Inspect | 1.3 | Inspecting encrypted traffic |
| ZTNA, MFA Server, JIT Access, SIEM correlation | 2.0 | Zero-trust and SOC foundations |
| Fleet Manager, sublicensing (MSSP) | 2.0 | Managing many customers from one place |
Objection and answer
Some objections are right. We admit them and offer a concrete condition instead.
True, and they are good tools. The question is different: how many hours a year it costs you to keep them running. Run the calculation above with your own numbers; in a pilot we measure before and after.
That is why the trial runs in shadow mode: traffic is not touched and the old firewall stays in place. The exit guarantee is in the contract, and under Early Access the move to 1.0 is free.
Correct: the product is not certified today, and we do not hide it. We start with organizations that do not require a certificate; for state universities, a trial deployment at no charge.
Correct: the first pilot has not finished yet. So the first customers get a separate condition: a discount in exchange for the right to use them as a reference and case study, with an anonymous option.
No. Forwarding, NAT, VPN, monitoring and logs do not depend on license state; only updates and support stop. This rule is checked on every change by a sabotage test.
The product works without internet: logs and settings stay in your installation, and the license is activated offline. A complete offline installation bundle is not ready yet and is planned.
The intended class is an x86-64 server with 4 cores / 8 GB RAM / SSD for a small office, and 8 cores / 16 GB for a mid-sized organization. Throughput figures are not published until they are measured on reference hardware.
One organization, one site, one gateway: install and shadow mode, an observation period, then cutover and a rollback drill. The success criterion is written down at the start of the pilot.
Trust
In a security product, trust is built not from advertising but from claims you can check. Every item in the left column is guarded by a test. The right column holds what has not been proven yet, and so is not promised.
QA-T-500 — on every change and every night
nft -c check and golden files
S02.5, cutover drill — in the lab
fsctl audit verify — chain test
S06.1, S06.5 — netns lab
This list gets shorter: when an item is measured, it moves to the left column and is updated here.
Plans
Price on request. The number of students or staff does not raise the price. During Early Access a discount off list applies, and the move to 1.0 is free.
Small office, branch
Price on request
fsctlMid-sized organization, university
Price on request
Bank, large organization
Price on request
In 1.1–2.0: WAF, remote access, TLS Inspect, ZTNA, SIEM correlation
Integrators
Price on request
From release 2.0
| Modules | Only modules that have shipped and been proven in a pilot; the list is an annex to the contract |
|---|---|
| Status | “Beta”: the limitation of liability and warranty disclaimer are stated plainly in the contract |
| Price | A discount off list; the move to 1.0 is free |
| SLA | Best-effort: P1 response within 4 hours, during business hours |
| Security | Internal security review; an external pentest is planned and has not been done yet |
In every plan: Telegram and email notifications, the audit log, the rollback log.
Next step
There is no form on this site: your message reaches us directly, and there is no button that falsely says “sent”. Write three things and we will plan together how the shadow trial connects: